December 11, 2024

Data Insights – Best Practices For Working With Your eDiscovery Partner

Subscribe to Our Newsletter

Newsletter


Kevin Skrzysowski

|

December 11, 2024

On Episode #30 of the Alternative Litigation Strategies podcast, host Kevin Skrzysowski sits down with author and technology evangelist W. Curtis Preston to discuss the latest eDiscovery challenges, strategies, and best practices for law firms and in-house legal departments.  Kevin and Curtis discuss what surprises lawyers the most about eDiscovery, the challenges of extracting backup information, the increasing complexity of dealing with mobile devices, and best practices for selecting and working with your eDiscovery provider. 

This transcript has been lightly edited for grammar and clarity.

Kevin Skrzysowki:

Welcome to the 30th episode of Certum Group’s podcast, Alternative Litigation Strategies, where I interview industry leaders in the legal marketplace from the top companies, firms, and academic institutions across the country. On this program, we discuss the latest trial strategies and trends impacting the litigation industry. I’m your host, Kevin Skrzysowski, a Director with the litigation consulting firm, Certum Group, where we specialize in working with businesses and their outside counsel to mitigate cap and transfer litigation outcome risk through our suite of finance and insurance solutions.

Today we have a very interesting program because we’re going to dive into a topic we’ve never covered on this program before, and that is the latest e-discovery challenges, strategies, pitfalls, and best practices that law firms should be aware of today. And to discuss this topic, I am pleased to be joined by W. Curtis Preston, AKA, Mr. Backup, a technology evangelist with S2DATA, an author of four books on modern data production, and the host of the podcast, The Backup Wrap-up. Curtis, thank you for joining the program today.

W. Curtis Preston:

Anytime, glad to be here.

Kevin Skrzysowki:

Curtis, maybe it would be a good idea if we started just by you telling us about the current business you’re involved in, S2DATA, and the range of services that you provide.

W. Curtis Preston:

So we like to talk about turning difficult things into opportunity. We tackle a lot of the really difficult technical problems that are behind a lot of different things. One part of the company specializes in the legal side of things, which is what we’re going to be talking about today, electronic discovery. On that side, we also do forensic services, imaging, every kind of computing type device, which is a giant tent that includes everything from a cell phone to a dash cam, right?

And then on the other side, we also work with IT departments that are managing their legacy data. So in our world, what that means is just as companies move forward in technology, they often buy new things, right? They buy new services, they move from this backup software to that backup software, and that leaves behind other sort of orphaned technology, which we call legacy technology. And then we help them manage the part of their company that perhaps a significant part of their IT department doesn’t know how to manage. So, we help with that as well.

Kevin Skrzysowki:

So really a full service, service 360 degree, e-discovery and computer technology services that you provide. Now, since we’re going to focus really on the legal industry today, can you tell us a little bit about what percentage of your client base are law firms and/or in-house counsel, and what are some of the particular services that you offer to them?

W. Curtis Preston:

Yeah, so I’m going to say it’s probably 60/40. That is a very unscientific number based on the fact that I don’t run the books. So based on what I see in the meetings, right? We spend a lot of time in our meetings talking about the various e-discovery services that we’re providing, and we spend a lot of time talking to lawyers, either in-house counsel, or third-party counsel to help people with those types of things.

And when we look at those, I’d say the biggest service that we’re providing is this, a client has been presented with an e-discovery request, and they either don’t have the resources to do it, or they are presented with a significant, and then we’ll talk about this, I’m sure, significant technical challenge in satisfying that request. Right? So we’ll step in and basically get all of the data that they need to get. We do that in such a way that we have a very documented and proven methodology, and we can then provide the data and we can provide an affidavit as to how that data was procured. And even depending on the client, even testifying on the stand if that’s necessary.

And then also very closely related to that but on the back end, very different, is this idea of forensic discovery. So if there’s a lawsuit or a potential lawsuit, then what we’re able to do is take, as I was saying before, phones, laptops, dash cams, security systems, any sort of thing that’s recording data and then storing it electronically. We can image that. One of the biggest things, I think there is text messages. So there are a lot of lawsuits that come down to who said what to when, and text messages are the modern equivalent to email. Email, of course, would be the biggest thing that we’re pulling out of a typical e-discovery request, but text messages you can retrieve directly from a cell phone.

And then we also have, as part of that service, one of the challenges is that when the text messages come out, they’re kind of ugly. They’re often in a spreadsheet, which is the way most people do it, but we’ve figured out a way to present them back to the client and therefore be able to present in court to look like the way they would have looked on the cell phone with… You’re familiar with the green on the left and the blue on the right, all that stuff?

Kevin Skrzysowki:

Sure.

W. Curtis Preston:

Preserving the order of the conversation and who said what and when and how, and we’re able to do that as well.

Kevin Skrzysowki:

Very interesting. I want to dive into some of the technical challenges that firms face and I want to talk a little bit more about specific challenges around text messages. But before we get there, can you just perhaps give us in just layman’s terms, an overview of what the e-discovery process really looks like?

W. Curtis Preston:

Yeah, so on your side, it’s pretty straightforward. We need all of the emails that Curtis wrote in the last five years that contain these three words, right? Or we just need all of the emails, we’re not sure what to look for but we need all of the emails written from Curtis to Steve. The requests can be all sorts of different filters. Before any discovery request comes in, a company is on a very regular basis, just any company or governmental organization, or a non-profit, they are most likely any reasonable company is backing up their data.

Kevin Skrzysowki:

Backing up the data, right.

W. Curtis Preston:

Yeah, on a regular basis they’re doing it, and they’re typically doing it actually every day, right? So you’ll do a full backup, which would back up everything. You do that every so often, and then every day you’re doing what we would call an incremental backup, backing up the data that’s changed. And you’ve been doing that and you hold onto that data for, in my opinion, far longer than you should, unless you have some sort of regulatory reason to hold onto it. But people will hold onto that data for five years, seven years, whatever, maybe even 10 years. And then you get this discovery question that says, we’ll pull out all the emails from Curtis to Steve.

The problem is that, two things, one is, again, speaking specifically in the US, right? The FRCP guidelines say that if you’ve got the data, you have to surrender it, right? It doesn’t say, well, if you’ve got the data but it’s in an inconvenient format, you don’t have to surrender it, right? But the problem is that the data is stored in backup format, which was never intended to be used as a source for e-discovery. It’s meant to be used as a way to bring back your server to the way it looked yesterday, or bring back your laptop because you dropped it and it shattered into a million pieces. That’s the purpose of backup.

And so when an e-discovery request comes in, the process of pulling the data out of these, just to speak specifically of email, pulling email out of the backup is an incredibly huge, very painful process that can take many, many months using many, many people. And also, a significant amount of resources from a technical perspective, meaning the hardware, the computers, and the storage and the tapes and the disks, all of that. It requires a significant amount of resource, much more than they would typically do in a typical week.

Kevin Skrzysowki:

And what I think I’m hearing from you is that there’s tapes and there’s disks, there may be cloud storage. So I know having worked for many legal information technology companies for last 20, 25 years, they invest or reinvest in different enterprise software and computer systems. I would imagine that these systems have changed over time and now you have to go back and try to extract that data from many different formats, from many different systems, through many different filters. Is that one of the main challenges?

W. Curtis Preston:

I’d say, yes, that is definitely one of the challenges-

Kevin Skrzysowki:

Sure.

W. Curtis Preston:

… in that, the more often you’ve switched up your backup technology, the more often you’ve changed it up. You talked about changing the backup software, you talk about moving to one of the big tape drives that we use, it’s called LTO. That’s easily the predominant tape technology for the last 10, 15 years. But there’s LTO-1, 2, 3, 4, all the way up to LTO-9, and you move forward in these tape drives in order to keep up with the latest technology. And you cannot read, for example, an LTO-1 tape and even an LTO-4 drive. There is a certain amount that you can do, but the more tapes you have and the more often you’ve changed it over the years, the more complicated the process becomes.

But the real challenge is not so much the hardware, it’s actually the software. Again, going back to what I was saying earlier, that the problem is that the format that it’s put onto tape or onto disk or in the cloud, the format was never written or stored in a way to allow you to retrieve it the way a lawyer is looking for. You go to pick your favorite backup software product with I’d say one exception, I can think of one backup product, if you purchase their extra feature that they have. Most backup products, if you go to it, there is no interface to go to say, give me all of the emails from Curtis to Steve for the last three years. It just doesn’t exist.

So what you end up having to do is, let’s say you’ve got a request for three years worth of emails. You go to three years ago and you restore your entire email system to the way it looked three years ago, and obviously you’re not doing this to your production system, you’re doing this to some alternate system. So of course this means more resources. You’re restoring it to that system and then you’ll extract from that system, you just start up this email server and you run a search against the email server for what it is that you’re looking for, and you create, a common format would be a PST file, in Exchange. So you create this Exchange file that contains the emails that you were looking for from three years ago, and this is going to take you many, many hours, maybe days, depending on your level of competence and resources you have available to you. And then you do three years minus a week ago, and you do the whole process again, and then you do three years minus two weeks ago, and you do the whole process again.

And so you’re doing, if you’ve got a weekly full backup of Exchange, which Exchange is a very common email backup system, if you’ve got a weekly full backup of Exchange, you’re looking at 52 times three, all restores of your system, followed by an extraction each time. It is an incredible process that needs a significant amount of hardware, a significant amount of time and expertise, because this is a very complicated process that you need to be able to defend in court. And so it’s just, the problem is really that you’re using a tool that was never designed to do what you need it to do in order to do what you need to do.

Kevin Skrzysowki:

It sounds like almost every matter almost takes a Herculean effort to compile all this so that it’s in a usable and digestible format and can be shared in discovery.

W. Curtis Preston:

I may sound like Henny Penny here, but it’s a significant effort. It’s so easy for a lawyer to say, “Hey, here’s the e-discovery request. Hey IT guys, go figure that out.”

The other part of this that, yes, just number one, it is a really difficult, technologically challenging problem because the product that you’re using to do it was never designed to do what you want it to do. But number two, you also typically have in today’s environment, IT departments with zero resources because they’re already stretched thin, and so they barely have the resources to accomplish what it is that they’re supposed to be doing. And then on top of that, you give them this Herculean effort.

So it’s a real challenge, and either one of two things happens. Either basically the IT department gets the significant impact to them and they’re able to do it in a, what a judge considers to be an acceptable amount of time, or they could actually take too long or make mistakes. So that would be the worst, is make mistakes along the way, and your risk is you get an adverse inference instruction from the judge that basically is the death knell of a lawsuit, right? Say, look, nobody could be this bad at reading their tapes, just assume that they’re trying to hide something, right? And there’s a famous case or infamous case with Morgan Stanley versus Coleman Holdings back in 2005 where that exactly happened and they lost a $2 billion lawsuit as a result. So, that’s sort of the problem.

Kevin Skrzysowki:

Now, and e-discovery has been around for a number of years, but I would imagine when you’re working directly with attorneys and you’re trying to explain how labor-intensive this is, how many resources it requires, how many different iterations of hardware and software you need to perform this function, they must be quite surprised at the length of time, especially when you’re dealing with lawyers, especially partners who are used to giving an assignment to an associate and say, “Draft this brief, or give me a reply and I need it by the morning.” Right?

W. Curtis Preston:

Yeah, here, go figure it out. Yeah.

Kevin Skrzysowki:

Do you find that this is incredibly surprising to lawyers and it’s challenging for them to digest?

W. Curtis Preston:

It is, it’s challenging for a couple of reasons. One, it requires understanding some rather technical nuances, right? And also, IT people, I mean, I love them, they’re my people, okay? I’ve been in IT for over 30 years. We kind of have a history of going, oh, that’s really hard. I don’t want to do it. Right? And so that doesn’t help. And so what they hear when an IT person is trying to say, “Look, what you’re asking me to do is actually really, really difficult.” I think the very natural response is to not believe it or to think that they’re exaggerating it.

And I guess what I’m trying to do, and by the way, I’ve always had this. I’ve worked for S2 now for about nine months, and it’s not like I’m just now singing this tune. I’ve been talking about this for years, that backup was never intended to do e-discovery. And what I’ve historically been pushing people to do is if they’ve got a reason to keep data for many, many years. To not use the backup system, to use a different kind of system, which is called an email archive system, but nobody’s been listening to me. So the vast majority of the IT departments, they don’t have the time or the budget to create an entirely separate system just in the, I don’t know what the… Hopes is the wrong word, in the thought that they might someday get an e-discovery request, right? They’ll just say, “Look, we’ll just do backup.” And then they also get surprised when they find out just how difficult it is. So yeah, IT departments are surprised. So the lawyers, if they’ve never interacted directly with their IT department with an e-discovery requests, I do think lawyers are quite surprised.

Kevin Skrzysowki:

And then how do you get the information so that it’s actually in a usable, shareable format in discovery? I mean, when lawyers are doing discovery, they do a request for production of documents, requests for emission interrogatories, and it’s simple like English prose, it’s just English language written down on a page and they can read the answers to it. When they’re doing an e-discovery and they’re trying to extract emails from many years ago that might be on a tape, what does the information look like when it comes out and how do you get it so that it just looks like written English language and can be shared during the discovery process?

W. Curtis Preston:

Yeah, so you need some type of format of a file that we can all agree on. Usually, 90% of the time we’re talking about Exchange, which is, it’s either Exchange or it’s Exchange replacement, which is Microsoft 365, which is their cloud version of that. But all of these can be exported into a format, a common format would be a PST. That is a format of a file that could be fed into a review platform that then allows them to sort and play with it and search against it easily. It is English. You can open up, you can take Outlook, which is a piece of software to read email, and you can open a PST file and you can look at it and it all looks normal and you see emails and you can search against it. But what most people are going to do is they’re going to take that and import that into a review platform. And there are several of those out there. But the hard part is getting it out of the very proprietary backup format and into that exportable format.

Kevin Skrzysowki:

Understood, okay. Now we’re talking about emails that are exchanged, or maybe there’s some other types of communication systems within the enterprise of the law firm or the corporate legal department. You had mentioned cell phones earlier, that’s a whole nother animal. I mean, those are not connected, hardwired to the communications infrastructure necessarily in a firm, right? These are going through another proprietary network of cell towers. How do you deal with that problem? And then, what about the issue where people might be using their personal phones for business use, and how does that fall under the guise of e-discovery, and what unique challenges does that present?

W. Curtis Preston:

Yeah, that’s a great question and there’s no easy answer, right? And I don’t think I have a good answer there, in terms of the personal cell phone. I will say that even if you’re using a personal cell phone for company work, the data that’s on that phone is still company property and I would think, this is more a legal question than a technical question, and that is that you could certainly attempt as opposing counsel, you could say, “I want everything that every time this guy was texting this guy, I want all those, even if it’s on personal cell phones.” And I would think that you would probably be able to demand that discovery.

Where I really come in is assuming that has happened, whether it’s a personal cell phone or a company’s cell phone, how do you get those messages? There’s two ways. One is, you can actually subpoena the communications company and potentially get the data that way. But another and probably more common way, and this is where we get involved, is you just get that phone. Right?

Kevin Skrzysowki:

You physically get the phone.

W. Curtis Preston:

You physically take that phone for a period of time and you extract directly from that phone. Again, this is highly specialized, requires very expensive software to extract that data off that phone. And then you have, you talk about human readable, it’s human readable, but it’s not very pretty. Think of a spreadsheet, which is what typically does, but we’ve figured out a way to present that in a much more human readable format, where it’s literally just an image that you can see who behind and what the conversation was.

Kevin Skrzysowki:

Almost like screenshots, yeah, like a rolling screenshot and reverse chronological.

W. Curtis Preston:

Right.

Kevin Skrzysowki:

Okay. So you’ve raised a lot of the unique challenges that law firms and in-house departments are facing today, and a lot of the pitfalls to try to avoid. If you were to sum up, just what do you think is the biggest challenge that is facing law firms today when it comes to e-discovery? And how does S2DATA solve it? What would that be?

W. Curtis Preston:

Yeah, so I’m going to say that it’s the format, the backup format that most of the data that you’re trying to extract is sitting in, right? It’s sitting in this very proprietary format on a tape drive or a disk or a cloud, and it’s in this weird format that most people are not going to be able to read. And then if you’re using the backup software to try to do it, the backup software was never designed to do it, so it doesn’t know what to do. And so like I said earlier, you’re presented with a Herculean task, I love your term there. Presented with a Herculean task of just doing it over and over and over again and extracting the data. It is a huge task to do.

The way we’ve figured out to do is we have figured out how to go directly at the data, basically just ignoring the backup software that wrote the data in the first place. We’ve written proprietary software that knows how to directly read the backup disk or tape where that data happens to reside, and we’re able to directly extract. You can tell us, “We’re looking for PDFs with this name, we’re looking for emails from Curtis,” and we can directly extract that and do this like as a… Before, remember how I said you have to do this full restore and then individual extractions? We’re able to do that as a single pass and do it much literally like an order of magnitude quicker for two reasons.

One is we have this proprietary software that’s written specifically for e-discovery. And two, that we have specialists that this is all they do. And three, we have a ton of hardware, whereas the typical IT department, they have just enough servers and tape drives and storage arrays, whatever it is that they’re using to get the backup done. They have just enough hardware to get the job, their normal everyday job done. We have an entire bank of tape drives that are just in robots and all that kind of stuff that are just sitting there waiting to do e-discovery requests. Right? So we can be doing simultaneous e-discovery requests for multiple clients, and we can automate it in such a way that it can run 24 hours a day. So it’s a purpose built system with a lot of extra hardware and people with expertise, is how we’re solving this problem.

And so, what the customer can do is they can literally say, “We have this e-discovery request. It looks like this. These are the things that we’re supposed to find. Here’s all our tapes, here’s all our disks, whatever it is, and just handle that for us.” And we actually have… Different clients, we work with different ways. Some are, they don’t want their data to leave their building, but some are fine with sending us their backups. We purchased a former bank, so we actually have a vault, an actual vault that we’re storing tapes in. So we take the tapes in, we can do it as a full service where you just send us your backups, we do with them what you want.

We also put all of the data, once we’ve scanned all of the tapes, we extract the metadata. There’s another technical term, so the metadata is all of the information about the emails, right? So the backups, when they were done, who they were from, all of that sort of stuff. We put that data, file names, all of that sort of stuff. We put that up into an online portal that can be searched against for further requests, or we can do this on premises for a customer that doesn’t want send their data out. But basically, you just outsource the entire operation.

Kevin Skrzysowki:

Understood. I mean, it sounds like with the proprietary software that you’ve developed, and I’m sure there’s a proprietary algorithm, my words embedded in there, so that you can complete the discovery request. The massive amount of infrastructure that you’ve built and the security that you have in your vault, you’ve really created a best-in-class e-discovery service for law firms and in-house counsel.

W. Curtis Preston:

Yeah, absolutely. And by the way, we even handle encrypted tapes. So for those that don’t know, when you write a backup tape, you can actually encrypt the backups as you’re writing it to tape, and actually the tape drive does that. There’s an encryption key that’s stored somewhere. You give us that key, and we can actually decrypt the tapes, again, without the backup software, which is very nice.

Kevin Skrzysowki:

And now that’s-

W. Curtis Preston:

So-

Kevin Skrzysowki:

… the forensics portion of your business?

W. Curtis Preston:

No, it’s just part of the backup. It’s just part of interfacing with a backup system. A normal backup software product, anytime it wants to interact with encrypted tapes, it has to pass the key to the tape drive and says, “Hey, I need to read this tape. Here’s the key,” and then the tape drive would decrypt it. We just do the same thing. Our proprietary piece of software, which is called TRCS, by the way, T-R-C-S, and it just basically pretends to be the backup software and says, “Hey, we need to read this tape drive. Here’s the key.” Right?

Kevin Skrzysowki:

Well, it sounds like you’ve created some very efficient solutions for very common problems that are plaguing the litigation marketplace. This has been a very interesting conversation, a lot of this I really was unaware of. As we’ve discussed, many lawyers are aware of the complexities of fulfilling and satisfying an e-discovery request. So, if you had maybe one piece of overarching guidance you could give to a firm or in-house counsel to help or to produce a best practices in e-discovery, what would it be?

W. Curtis Preston:

It’ll sound self-serving but it’s still my best advice, and that is, don’t do it yourself. It’s far more complex than you think it is. It’s far more expensive than you think it is to do it yourself. You think you’re saving yourself money by doing it yourself, but it will extend the time out significantly to the point that depending on how things go, you could end up looking like you’re trying to hide something to a judge. And that is, as I mentioned earlier, it’s a disaster. Right?

Kevin Skrzysowki:

That is not good.

W. Curtis Preston:

So if you’ve got a company like S2DATA that can do it for you, it will save you money in the long run and potentially actually help win the case. Now, here’s a perfect thing. Everybody thinks they’re innocent, right? Everybody thinks either they didn’t do it. There’s a million innocent people in prison, right? No company wants to think that they’re the ones that did the thing. They want to thank that the smoking gun email is not there. If that’s truly the case, having a third party go and search all of your backups thoroughly with a proven methodology documented, that you then have either an affidavit or someone testifying on your behalf to say, “Look, this is what we do for a living. We have searched all of the backups. The smoking gun email isn’t there.” That, there’s nothing more powerful than that from a defense standpoint.

Kevin Skrzysowki:

What you’re providing to that business, you’re proving it and you’re giving them the certainty that backs up their belief that they truly are innocent or not liable or right. Right?

W. Curtis Preston:

Absolutely.

Kevin Skrzysowki:

I think that’s an excellent point to finish up on. Well, Curtis, this has been a really interesting conversation. I want to thank you for joining the program today. I appreciate all of the really interesting and valuable insights you provided into the world and the technical challenges of e-discovery. Thanks for being on.

W. Curtis Preston:

Anytime.

Kevin Skrzysowki:

Now, if any members of the audience or any firms or in-house counsel who are listening to this podcast would like to get a hold of you, what would be the best way to reach you?

W. Curtis Preston:

So I’m CPreston@S2data.com. That’s S2, the number two, data.com. We actually have an offer on, so if you go to S2data.com/podcastoffer, I created a, basically, if you’ve got… So many people have a drawer of tapes, a pile of tapes, and they don’t know what’s on them. And you’re like, can these people really just scan my tapes and figure them out? And the answer is, yes. So we have an offer if you go to that, basically, we’ll scan one of those for you for free to show you what we can do and show you how easily we can solve that problem for you.

Kevin Skrzysowki:

I think that’s a great offer. Thanks again for being on, and of course, as always, I want to thank the audience for listening. If you’d like to hear more, please be sure to follow us on Apple, Spotify, Stitcher, or anywhere you listen to your favorite podcasts. And if you’d like to learn more about the litigation, insurance, and funding solutions that Certum Group provides, please visit our website at www.certumgroup.com. That’s C-E-R-T-U-M Group, or you can always reach out to me at KevinS@certumgroup.com. And until next time.

Certum Group Can Help

Get in touch to start discussing options.

Recent Content

By Patrick Dempsey • September 29, 2026
This is the third post in Certum Group's seven-part series bringing our Trade Secret Litigation Playbook to the blog. It draws on Part III of the Playbook, Before You File. Read or download the full Playbook here . The call usually comes from a sales leader, a head of engineering, or a chief of staff, and it usually starts the same way: "We think someone took X, and we think they took it to Y." What happens in the next three days is disproportionately important. The most expensive mistake in trade secret practice is waiting — every week that passes lets the defendant commercialize your advantage, and worse, lets the evidence quietly disappear. Slack messages, badge records, and git histories often sit behind auto-delete settings as short as ninety days. So before you do anything else, move to preserve. Here is what good early triage looks like. Issue a litigation hold — in writing, within 24 hours A written instruction to preserve any document, chat, email, calendar, or file relating to the possible misappropriation, sent to the full legal, HR, IT, and leadership teams. It should be specific enough to be useful, broad enough to catch the unexpected, and documented enough that you can produce it later. This is the single most important thing you can do in the first day. Lock down forensic images — and don't let internal IT do it Laptops, phones, and company devices belonging to any suspected party should be forensically imaged by an outside forensics firm, not wiped or "checked" by internal IT. Chain of custody matters, and internal teams generally cannot testify to it at trial. The right instinct is to image broadly and review narrowly: you can always decline to look at a device you preserved, but you can never go back for one that was reissued, wiped, or sold. And don't forget the non-obvious sources — personal cloud drives, USB connection histories, printer spooler logs, and screen-capture utilities are often where the decisive evidence actually lives. Extend retention on cloud and platform logs Have IT extend retention on the relevant accounts and export the log data — access logs, download histories, egress traffic — before anything rolls off. The forensic story of who did what, when, and with which file is usually more persuasive to a judge than any human witness. A download at 11:47 p.m. the night before a resignation is powerful evidence because of what the timing means. Do not tip off the adversary Resist the urge to confront the suspected employee, their new employer, or their counsel. Confrontation at this stage tends to accelerate deletion and pull communications behind privilege claims. A carefully timed cease-and-desist letter, sent after preservation is secure, is a very different move — and a far more effective one. Investigate under privilege Any investigation you run should be conducted under attorney direction, so that the work product is privileged and your witness interviews do not become admissions used against you later. This is not about secrecy for its own sake. It is about making sure the investigation helps your case rather than becoming evidence in it. Consider — but do not rush — the early public filing Ex parte seizure orders, temporary restraining orders, and preliminary injunctions all have their place, and an early injunction can be the single most valuable outcome in the whole case. 1 But these motions require a level of evidentiary support you rarely have on day three. It is almost always better to spend a week building the record than to file fast and lose the first motion, which hands the defendant a narrative and hands you a hole to climb out of. The triage checklist If you want a single page to keep by the phone, it looks like this: litigation hold issued in writing within 24 hours; outside forensics firm retained and imaging scheduled; cloud and platform log retention extended; a list of suspected individuals plus their managers and peers; a list of the specific secrets that may have been taken; copies of every NDA, employment agreement, and IP assignment covering them; a review of the last 90 days of their calendar for unusual patterns; and outside trade secret counsel engaged under privilege. Do the first 72 hours well and you preserve every option that follows — injunction, damages, settlement leverage. Do them poorly and you may spend the next two years litigating around evidence you could have saved in an afternoon. If you are in the opening days of a matter and want a fast, confidential read on what to do now versus later, that is exactly the conversation we have most often. Go deeper with the Playbook. This post covers one piece of a much larger picture. For the full framework — what the law requires, what a strong pre-filing case looks like, how damages experts value these matters, how counsel fee structures change your economics, and how litigation finance fits in — read Certum Group's Trade Secret Litigation Playbook , our field guide for business owners and the counsel who advise them: certumgroup.com/the-trade-secret-playbook . And if you are evaluating a live dispute — or simply want to pressure-test what a matter is worth and how it might be funded — get in touch. A confidential conversation with Certum is free and carries no obligation, whether or not you ultimately seek funding. Reach us at certumgroup.com/contact-us . Sources 1. The ex parte seizure procedure is authorized by the Defend Trade Secrets Act, 18 U.S.C. Section 1836(b)(2), and is available only in extraordinary circumstances.
By Patrick Dempsey • September 15, 2026
This is the second post in Certum Group's seven-part series bringing our Trade Secret Litigation Playbook to the blog. It draws on Part II of the Playbook, Trade Secret Law in Plain English. Read or download the full Playbook here . Here is a statistic that surprises most executives: in federal trade secret cases that reach a verdict, plaintiffs win roughly 84% of the time. 1 That is dramatically better than the plaintiff win rate in commercial litigation generally. It does not mean every case is easy — the cases strong enough to reach a jury are a selected group — but it tells you something important about what happens when a well-built trade secret claim gets in front of a fact-finder: courts tend to enforce the rights the statute was designed to protect. So why do good claims still fail? Usually not at trial. They fail earlier, on assumptions the claim holder never stopped to test. In more than a decade of evaluating these matters, the same handful of misconceptions come up again and again. Here are six worth clearing up before they cost you a case. Myth 1: "It's only a trade secret if we stamped it CONFIDENTIAL." Marking helps, but it is not required. What matters is whether your overall secrecy program is reasonable under the circumstances — a holistic look at contractual, physical, and technical controls. A perfect stamp on an otherwise open system is worth less than a coherent program with a few gaps. Myth 2: "If part of it is public, none of it is protected." Courts routinely protect a combination of individually public facts when the particular combination delivers competitive advantage. The recipe can be assembled from ingredients anyone can buy. What you protect is the assembly. Myth 3: "Our employees signed NDAs, so we're covered." NDAs are a foundation, not a program. The full set of reasonable measures a serious claim holder is expected to have includes access controls, badging, egress monitoring, exit procedures, and technical segmentation. An NDA in the drawer and nothing behind it is exactly the gap a well-resourced defendant will press on first. Myth 4: "We didn't sue the last person who left, so it's too late now." Trade secret protection is evaluated case by case. Declining to act on one departure does not forfeit your rights as to the next one. Every matter stands on its own facts. Myth 5: "We're too small to enforce against a big company." This one gets the economics backwards. A well-funded claim against a large, solvent defendant is often easier to win — and easier to collect — than a disorganized claim against a small one. Resources can be added to a strong case; facts cannot be added to a weak one. The right capital partner exists precisely so that a smaller plaintiff can stand toe-to-toe with a much larger adversary and neutralize the outspend-them tactics that used to decide these fights. Myth 6: "It's just know-how — courts don't protect that." Courts protect integrated know-how constantly. The question is never whether know-how is capable of protection; it is whether you can identify it with enough particularity to describe what was taken. 2 That is the single most consequential early decision in the case, and it is the one most claim holders do not realize they are making when they plead "our proprietary software" instead of the specific, described combinations that actually give them an edge. The through-line Notice what these myths have in common: each one leads a claim holder to under-invest in a case that the numbers say is very winnable. The 84% figure is not a promise. It is an invitation to take the early work seriously — the secrecy program, the identification, the evidence — because that work is what turns a strong set of facts into a strong case. Get those right, and the law is on your side more often than in almost any other kind of commercial dispute. Go deeper with the Playbook. This post covers one piece of a much larger picture. For the full framework — what the law requires, what a strong pre-filing case looks like, how damages experts value these matters, how counsel fee structures change your economics, and how litigation finance fits in — read Certum Group's Trade Secret Litigation Playbook , our field guide for business owners and the counsel who advise them: certumgroup.com/the-trade-secret-playbook . And if you are evaluating a live dispute — or simply want to pressure-test what a matter is worth and how it might be funded — get in touch. A confidential conversation with Certum is free and carries no obligation, whether or not you ultimately seek funding. Reach us at certumgroup.com/contact-us . Sources 1. Stout, Trends in Trade Secret Litigation (2024), reporting an approximately 84% plaintiff-favorable outcome rate across 271 federal trade secret cases reaching a verdict since 2017. 2. Both the federal Defend Trade Secrets Act (18 U.S.C. Section 1836) and the state Uniform Trade Secrets Act define a trade secret as information that derives independent economic value from not being generally known or readily ascertainable, and that is the subject of reasonable measures to keep it secret.
By Kevin Skrzysowski • September 10, 2026
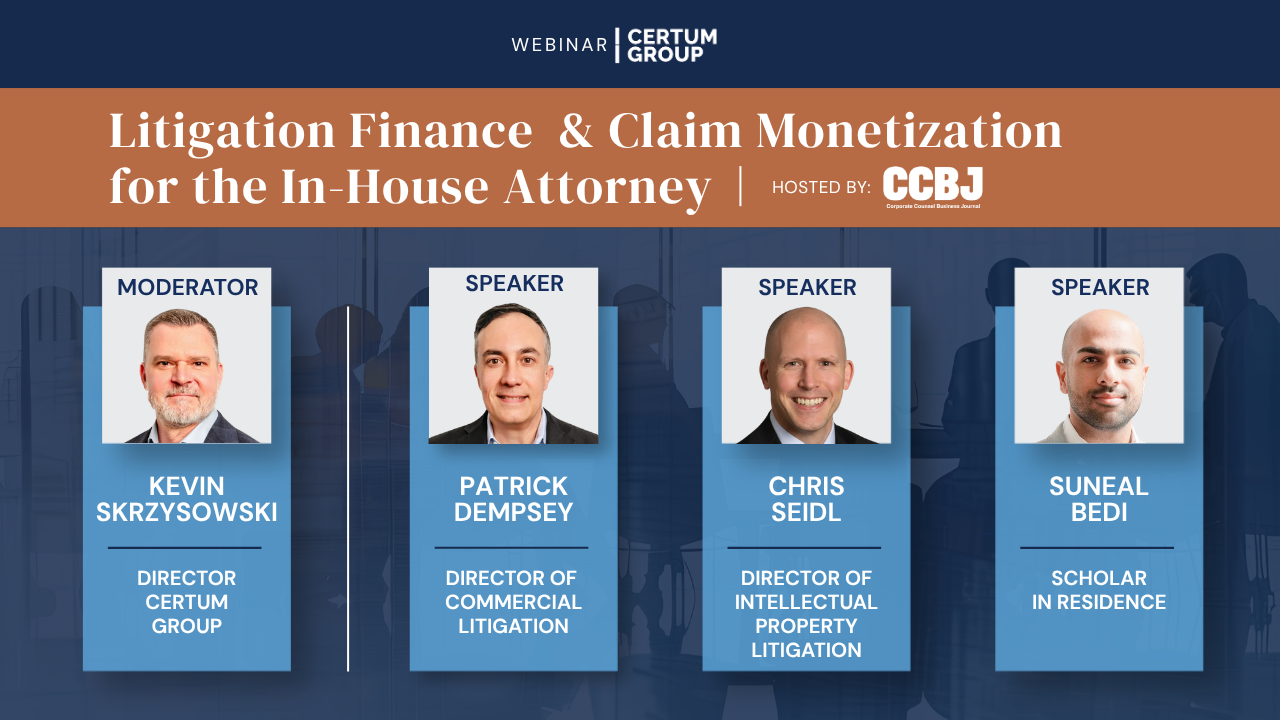
For most companies, the legal department is viewed purely as a cost center—a line item to be managed and minimized. But many organizations are sitting on significant, unrealized value in the form of affirmative claims: lawsuits they could bring against suppliers, vendors, or competitors who have breached a contract, stolen trade secrets, infringed intellectual property, or otherwise caused recoverable damages. All too often these valuable claims go unpursued because litigation is expensive, unpredictable, and competes with the business for budget and headcount. Certum Group, in conjunction with the Corporate Counsel Business Journal, created this one-hour webinar to show in-house counsel how litigation finance changes that calculus— allowing companies to pursue meritorious claims with little or no out-of-pocket cost and on a non-recourse basis, so the downside risk shifts to the funder while the company retains the upside. Our panel brought together leaders in commercial litigation, intellectual property litigation, and legal academia and demystified how litigation finance works and walked through practical, real-world uses for the corporate legal team. We also took a close look at claim monetization: the ability to receive cash today against the value of a pending or contemplated claim, rather than waiting years for a judgment or settlement. Monetization can take the form of an upfront advance secured by the expected recovery, or an outright sale of the claim to a specialized organization that then prosecutes the case and collects the judgment. Attendees left with an understanding of when litigation finance and monetization make sense, how to evaluate and pitch a case, what to expect from the process, and how these tools can transform the legal department from a cost center into a genuine contributor to the bottom line. Watch the full webinar replay HERE . Supporting Materials: Litigation Finance Guide In-House Survey Research Brief Trade Secrets Playbook